Readiness

Understand where your evidence stands — before an inspection, not during it.

Readiness from live governance records, compared across services and organisations. Counts and status you can check, never a black-box score.

www.assuraflow.io/dashboard/risk-radar
AssuraFlow
ReadinessRisk RadarSignals
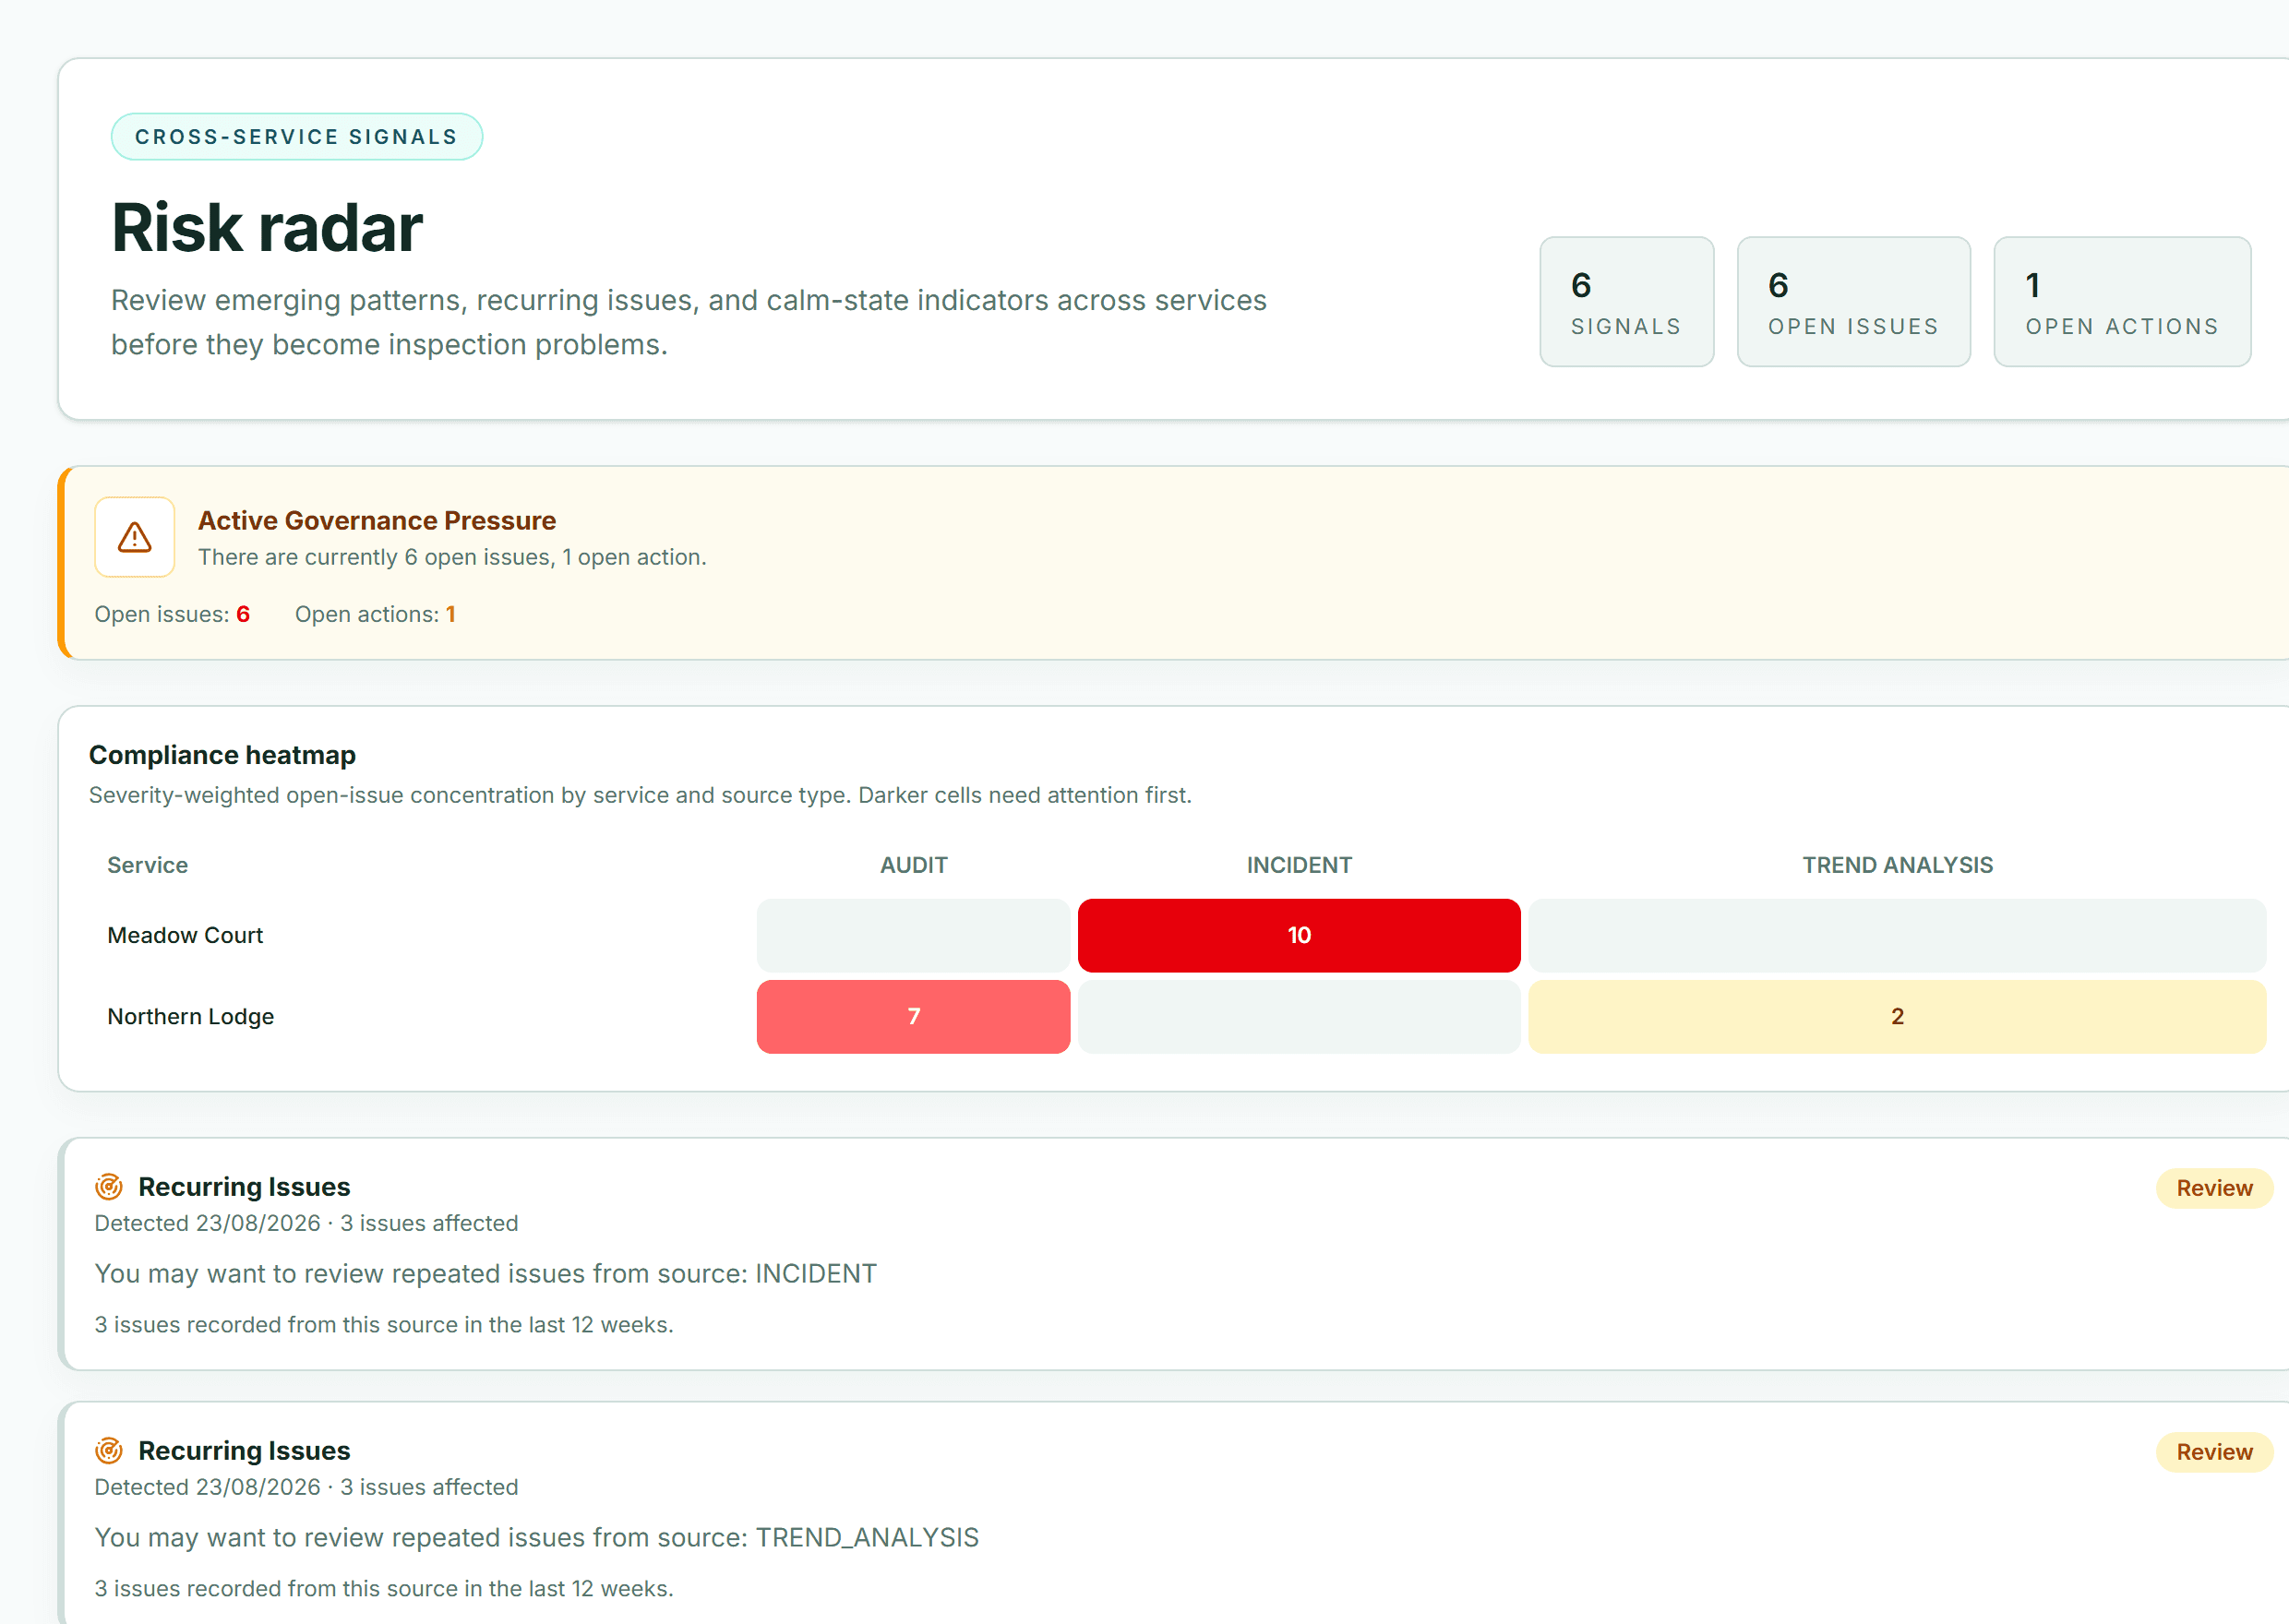
AssuraFlow risk radar — a severity-weighted risk heatmap by service and issue source

Evidence Readiness

A snapshot of whether your evidence is complete, partial, or missing across seven governance areas. No scoring — just visibility.

  • 7-area readiness assessment
  • Complete ✅ / Partial ⚠️ / Missing ❌ indicators
  • No scoring or compliance ratings
  • Derived from live data

NI/RI Control Tower

A Nominated or Responsible Individual who is accountable for more than one organisation gets one login across all of them — a live roll-up of open issues by severity, overdue actions, audits in progress, and Reg 44/45 visits due, per organisation. Each organisation grants and ends the engagement independently; ending it removes that organisation's data from the view immediately, and there is no separate charge for the NI/RI.

  • One login spanning every organisation you are the NI/RI for
  • Live per-organisation counts — issues, actions, audits, visits, training currency
  • One click to switch into an organisation and work on its records
  • Each organisation keeps ownership of its records and its own subscription

Benchmarking

Compare open issues, overdue actions, and training currency across the services in your organisation — raw counts side by side, not a single composite score.

  • Per-service open-issue severity breakdown
  • Overdue-action comparison across services
  • Training-evidence currency by service
  • No black-box compliance grade

Multi-Provider Group Oversight

For care groups running several separate provider accounts, a dedicated Group Admin role sees the same open-issue, overdue-action, and training-currency comparison rolled up across every account in the group — aggregated counts only, structurally unable to reach any single account's detailed governance records. Part of the Enterprise plan.

  • Cross-provider benchmark for group-level oversight
  • Aggregated counts, never individual governance records
  • Group Admin role scoped to its own group only
  • Group membership managed by platform administrators

Risk Radar

A severity-weighted risk heatmap across your services and issue categories, so recurring themes and high-risk services surface before they become an inspection finding. On the Growth and Enterprise plans.

  • Service × issue-category heatmap
  • Severity-weighted scoring, not raw counts
  • Cross-site pattern detection
  • No black-box compliance grade

Custom Audit Templates

Build your own audit and inspection templates — sections, question types including multiple-choice, evidence rules, and required/critical flags — then publish or clone them across services.

  • Section and question builder
  • Text, checkbox, date, and multiple-choice questions
  • Evidence rules and required/critical flags
  • Publish and clone across services
  • Optional regulator tag, filterable across your template library
  • Opt-in redaction of structured identifiers (NI number, NHS number, email, phone, postcode) on export

Reg 44/45 Visit Scheduling

Track when the next independent-visitor review (Reg 44) or quality-of-care review (Reg 45) is due per service. Starting a visit runs the full audit-template checklist, evidence, and staged sign-off — the next visit schedules itself once that one's signed off.

  • Per-service cadence tracking, configurable
  • Starting a visit begins a real, evidence-backed audit run
  • Next visit auto-scheduled from the actual sign-off date
  • Surfaces on the Planner alongside every other deadline

Commissioner Readiness Access

Give a commissioning local authority a private, time-limited, read-only link to an inspection-readiness summary for the services it commissions — service status, ratings, and open-issue counts only. No person-level records, and no incident, complaint, safeguarding, or financial detail.

  • Per-authority link, scoped to named services and a fixed expiry
  • Counts and status only — never underlying records
  • Revoke instantly; every view is audit-logged
  • Opens with no account, on any device

Longitudinal Continuity

Time-based views across any governance area. See what happened, what was done, and what changed over weeks and months.

  • Configurable time window (1–12 months)
  • Regulation-area filtering
  • Chronological event timeline
  • Open vs closed case totals

Request a platform walkthrough

Share your operating model and receive a tailored demonstration of relevant workflows.